Pages

Tuesday, 29 May 2018

Steps to Eliminate IDLE DRIVER.EXE from the PC

Threat Summary of IDLE DRIVER.EXE


  • Name: IDLE DRIVER.EXE 
  • Threat type: Trojan horse
  • Infected OS: Windows-based system
  • Risk level: High
  • Symptoms: Consume lots of system resources, slow down the PC, steal privacy, etc.
  • Removal Process: Remove with manually or automatically


IDLE DRIVER.EXE is categorized as Trojan horse which stealthily intrudes in the PC without user’s acknowledgement. It assists other dubious programs to invade the PC. It is mainly created by cyber criminals with the sole purpose to make online benefit from the infected users. IDLE DRIVER.EXE is so nasty that continuously consumes lots of space of CPU resources and makes your PC sluggish. Once infiltrates, it detect your entire files remotely and steal all confidential data to make illegal money. Moreover, this Trojan cal alter browser settings of your working browser and display lots of ads and pop-ups to irritate the users.


IDLE DRIVER.EXE is infiltrated in the system via peer to peer sharing of file or network, clicking on infected ads, bundled with third party application of program, via infected media, watching online movies and visiting unwanted sites like torrent and porn sites. After getting into the PC, it will slow down the system speed and drop a malicious code in the registry editor for automatic start-up. It can also disable the security program like anti-virus and Window Firewall to hide in the system for the unknown time. Therefore, you should try to make your PC safe and remove IDLE DRIVER.EXE infection from your PC immediately.


Sunday, 20 May 2018

Effective Method to Get Rid of 1-888-279-3119 Pop-up from the PC

1-888-279-3119 Pop-up is the perilous pop-up infection that claims users that it is the legitimate and genuine tech-support service which provide helps for users. It is mainly categorized as an adware or Scam Alert and it targets primarily Windows-based system. Once it gets inside the pc, it will display a fake pop-up and tells users that your system is infected with harmful viruses. They also urge the users that if you want to remove harmful viruses from your PC then you need to call on tech-support service number given on pop-up. Be careful, it is a scam virus and if you make a call then you may suffer huge financial loss. Moreover, it also alters the browser settings and display lots of pop-ups and ads that cause interruption in browsing session of the users.


1-888-279-3119 Pop-up is generally spread via spam email attachments, flash player, fake software update4s, p2p file or network sharing, clicking on malicious ads, visiting unwanted sites like porn and torrent sites and much more. Through this pop-up infection, scammers monitor you internet activities and track surfing details. This infection can steal your privacy and disclose to the scammers for illegal use. Therefore, it is highly suggested you to remove 1-888-279-3119 Pop-up from the PC as soon as possible.


Tuesday, 15 May 2018

Manual Process to Remove Gorlita.com from the PC

What is Gorlita.com?

Gorlita.com is the dubious redirect virus that belongs to the browser hijacker category. It is mainly created by cyber hackers with the only in tention to scam the innocent users. It silently infiltrates the system without user’s permission.

How this redirect virus infiltrates the system?


This cunning infection primarily infiltrated via spam email attachments, via fake software updates, clicking on infected ads, bbbundled with third-party software, visitnng suspicious sites like porn and torrent sites and so on.


What are the harmful impacts of Gorlita.com?

Once this redirect virus installed on your browser, it will take full control of your working browser and alter its settings including home page, new tab page and redirect your search result to the malicious domain. After redirection, it will display lots of misleading ads and ppopp-ups or banners that promote the third-party products and collect revenue from innocent users for sponsored links. 

Which OS does it mainly infecft?

It particularly targets the all version of Window-based system and useful web browser such as Google Chrome, Mozilla Firefox, Internet Explorer, Microsoft Edge and Safari.

Is it suitable for the Privacy or not?

No, it is not safe for the privacy. This virus collects the lots of sensitive information and disclose to the crooks for misuse. They can monitor your online activities and steal the privacy for misuse.

What can this infection do after infiltration?

After infiltration, it will mess up with DNS configuration and makes lots of copies of registry entries to achiever high-level persistence. It can also able toi disbaqle your entire security tools to be undetected. Gorlita.com is so nasty that it caqn consume lots of space of system resources like CPU and memory that degrade the performance of PC.
  
Tell me some method to remove Gorlita.com from the PC?

It us highly-sugge4sted thqat never open junk emails from unknown senders and nevcer install or download software from third poarty sites. Read Ennd User Licence Agreement (EULA) carefully before installation. Therefore, you should advised to remove Gorlita.com immediately from the infected browser. 


Friday, 11 May 2018

How to Remove +44-808-169-1446 Pop-up from the Infected PC


+44-808-169-1446 Pop-up is the fake tech-support number which is categorized as an adware or Scam Alert. It is mainly created by cyber scammers with the sole intention to scam innocent users. Once it gets infects the PC, it will display a fake pop-up notification which tries to convince users that your system is infected with different viruses and is at great risk. It notifies users to call on tech-support number like +44-808-169-1446 +44-808-169-1446 Pop-up. Furthermore, this scam virus alters your browser settings and display lots of intrusive ads to interrupt the browsing period of users.


+44-808-169-1446 Pop-up is infiltrated in the system with the help of bundling of software, clicking on malicious ads, spam email attachments, p2p file sharing, via infected media, playing online games, visiting unwanted domain like porn and torrent sites and so on. After infiltrating the system, it messes with the DNS configuration and system settings and drops a malign code in the registry editor that can additionally install dubious malware programs in the system. This fake pop-up disables the firewall security to hide in the system for a long time.

Experts say that never try to install or download any type of software from the suspicious source. Read terms and condition carefully before downloading the software. Try to eliminate +44-808-169-1446 Pop-up from the PC as early as possible.


Tuesday, 8 May 2018

Complete Removal of FacexWorm Virus from the PC

Are you got infected by FacexWorm Virus? Is your system doing strange behavior? Is this virus interrupting your working session? Is this worm infection altering browser settings and display lots of annoying ads? Are you immediately wanted to remove this infection from your system? Doesn’t worry, this guide help you to get rid of FacexWorm Virus from your system.


FacexWorm Virus is the dangerous infection that belongs to Trojan horse family. It is a type of malware infection named as worm virus which is created by cyber crooks with the only intention to harsh the innocent users. It silently gets inside the PC with the help of other malware programs installed in the system. Once it enters in the system, it will cause lots of malicious malevolent activities in the system and destroy some of system files that may crash the system. However, it has also ability to alter the browser settings of your useful browser and cause redirection problem. After redirecting to the malicious link, this Trojan will display lots on annoying ads and pop-ups that interrupt the browsing session of the users.

Moreover, FacexWorm Virus brings lots of other malware infection such as Rootkits, Keyloggers, worm, spyware, adware and even deadly ransomware that makes your PC as malware hub. FacexWorm Virus is infiltrated in the system through bundling of third party software, via infected advertisements; downloading videos and movies from torrent, junk emails, via infected media and so on. Additionally, it will mess up with system settings and modify registry editor for automatic start-up. It consumes lots of CPU resources and makes PC sluggish. Thus, try to remove FacexWorm Virus immediately from the PC.


Saturday, 26 November 2016

Remove Gotowebs.com Completely From Infected PC


Gotowebs.com is recognized as browser hijacker which pretends to be a search engine. It can find its own way to invade in the system and carries ability to mislead the users. It can perform changes in the system settings and tries to gain the full control of the system. Gotowebs.com will appear as your default homepage and forces the users to download free software. It is capable to flood the screen by showing unwanted pop ups and advertisements on the screen which are completely fake in reality. It will become extremely difficult for the users to surf normally on the web. You will also detect sluggish speed of the system functions in which working is quite difficult. Even more, it have capability to steal and bypass the credential data of the users to the remote servers. So, don’t allow Gotowebs.com to stay for long time in the infected PC.


Sunday, 6 November 2016

Remove Trojan:WIN32/Vundo.LPX Completely From Infected PC


Technical Description Of Trojan:WIN32/Vundo.LPX:
  • Name: Trojan:WIN32/Vundo.LPX
  • Type: Trojan
  • Wild Level: Severe
  • Geographical Distribution: High
  • Affected Operating System: Different versions of Windows

Trojan:WIN32/Vundo.LPX is considered as malignant Trojan infection which posses worst impacts on the system performance. It can invade in the system without the users consent and performs malicious activities. Trojan:WIN32/Vundo.LPX have capability to hide its presence under the internal files which is difficult to detect manually. Even its worst impacts can disable the working of security tools such as antivirus as well as Windows Firewall. This threat has damaged million of PC across the world and its geographical distribution is very high. It is also responsible for modification in registry entries, system slow down, unwanted changes, crashing of PC and many more. Besides this, it have ability to keep its eyes on the online activities of the users and send the collected data to the remote hackers. So, if you don’t want to face all these troubles then remove Trojan:WIN32/Vundo.LPX without making any delay.


Tuesday, 4 October 2016

Remove Al-Namrood Ransomware Quickly From Infected PC


My system has been infected with Al-Namrood Ransomware. I tried to remove it manually but failed. It has encrypted my files and asks me to pay the ransom amount. Please help me to remove Al-Namrood Ransomware completely from the system. What can I do now to restore my important files which has been encrypted by Al-Namrood Ransomware? Please help me!


Al-Namrood Ransomware is a file-encrypting ransomware which can  which has been designed to encrypt files, documents, database files, images, videos etc. It will append “.unavailable” extension in all the files after the encryption process. For example, if your file was saved with sample.png then Al-Namrood Ransomware will change it to “sample.jpg.unavailable”. This ransomware can penetrate in the system when user download or click on the spam email attachments. After the encryption process, it will create a text file on the desktop which contains some instructions. The file will inform the users that their files has been encrypted and if they want to restore them then they need to purchase the decryption key. 

Al-Namrood Ransomware displays that only unique key will help you to restore the files which is available on a private server. It asks the users to pay $500 in Bitcoins to obtain the key. Users needs to be aware that it is just a scam of the third party hackers which should not be trusted at any cost. Recently, Al-Namrood Ransomware has been detected by the users of Saudi Arabia. It only tries to frighten the innocent users and tactics on them to pay money. The worst part is that even payment will not help you to restore the encrypted files. By sending money, you will only help the hackers to enhance their business. It will also affect your personal identity as they are capable to steal your personal details by tracking the online payment. Hence, you need to remove Al-Namrood Ransomware immediately instead of making online payment.


Sunday, 2 October 2016

Step-By-Step Instructions To Delete Trojan.Ransomcrypt.AW


Trojan.Ransomcrypt.AW is deemed as Ransom Trojan which is completely destructive from nature. It has been created by the hackers and spread over the web. This threat doesn’t need any permission from the administrator to sneak in the targeted system. Existence of Trojan.Ransomcrypt.AW will encrypt your files and it can lock your PC screen. It will create ransom note on the desktop and asks the users to pay the amount to restore the files. Do not follow any of its instructions because it is just a scam of the third party hackers whose main motive is to trap the users. They are capable to track your online activities and record all the sensitive information which you will type while making payments. Thus, you should try to remove Trojan.Ransomcrypt.AW in the initial stage after detection.

Trojan.Ransomcrypt.AW posses worst impacts on the system efficiency. In the early phase, it tries to gain full control of the PC by changing the privacy settings. Even its harmful impacts can also modify the processes of anti-virus program to hide its presence for long time. You will notice weird behavior of the system in which normal working is quite difficult. This threat can generate bogus processes in the task manager which can increase the CPU utilizations. It will directly affect the running speed of the system and Internet connection. Crashing of the operating system, BSOD alerts, modifications in default settings will become a common issue in its presence. Its long time existence can leads the system to critical situations or make it completely useless. Hence, if you don’t want to face such troubles in your PC then take immediate action in the removal of Trojan.Ransomcrypt.AW completely from the system.

Remove Ulrtep.com: Complete Guide To Protect PC From Ulrtep.com

Ulrtep.com is yet another detection in browser hijacker category which can mislead the Google, Yahoo or Bing search results of the users to its own homepage. It can attack the system when you will click on suspicious links or visit malicious pages. Ulrtep.com have capability to install itself in the browser by changing the default settings. It will also drop fake extensions, plug-ins, add-ons or toolbars in Chrome, Firefox, IE, Opera, Safari etc. When you will launch the browser, it will automatically divert you to Ulrtep.com and the screen will be filled with unwanted ads, pop ups, in-text links, contextual links, banner ads etc.


Ulrtep.com also shows attractive deals, offers, discount coupons etc on the screen which looks attractive at the first glance. It uses malicious tactics and convince the users to shop from its links. You need to know that hackers will secretly keep their  eyes on your online habits. When you will enter any sensitive details related to bank account or passwords then they will steal them without your consent. They can use your data in illegal purpose which is not safe for your personal identity.

The main objective of the cyber crooks is to increase traffic of Ulrtep.com through illicit ways. They will get earn commission on every click or download. Besides this, it posses worst impacts on the PC performance. The running speed of all the functions such as start up, shut down, opening files, playing games, installing applications, Internet connection etc. It will also affect the working of installed PC security programs including anti-virus, Windows Firewall etc. Users will receive warning alerts when they will attempt to visit any of the genuine pages. Permanent freezing of the operating system is also possible in its long time existence. So, if you don’t want to pay heavy penalty in future then remove Ulrtep.com as soon as possible.


Get Rid Of Dnav.com: Remove Dnav.com Completely From The PC

Recently, many users have complained that their search results automatically gets diverted to Dnav.com. If you are one of them and wants to know that why are you facing such situations then you have landed on perfect location. You just need to follow the post which is given below. It will provide you detailed information about Dnav.com and the best way to stop redirection problem.


Things to known about Dnav.com:-

Dnav.com is recognized as suspicious domain which may seems like a genuine site. This page contains various download links, advertisements, banner ads. You should know that clicking on such links will make your compromised. Dnav.com is identified as browser hijacker which have capability to hijack the system. Mostly, it attacks different versions of Windows and gets installed as an extension in Google Chrome, Firefox, Internet Explorer etc. You will not be able to visit any site of your choice due to automatic redirection. You may also detect alterations in the homepage settings and browser settings. 

Dnav.com brings lots of damage to the system in which normal working is extremely difficult. It can use your Internet history to display advertisements and pop ups. These alerts will claim to save you money or allow to download freewares but reality is completely different. Hackers only aims to drive more traffic on their suspicious pages by redirecting the users. They also tries to increase the sales of their affiliate products in order to earn commission. Downloading free software from links can bring harmful threats such as spyware or malware in the system. So, we strictly suggest the users to remove Dnav.com immediately from the system.

Besides this, the extensions of Dnav.com will steal your cookies, banking details,, passwords or other credential data and bypass them to the remote servers. It is not safe for your personal identity. Users will also get error messages when they will try to perform an task or open the stored files. The overall performance of the compromised PC will become extremely sluggish  and most of the files will become inaccessible. Lots of changes in the default settings is also possible. Its presence can result to regular freezing of the browser and crashing of the operating system. So, don’t waste a single moment in removing Dnav.com permanently if you want to protect your system.

Uninstall Backdoor.Hynet: How to Get Rid of Backdoor.Hynet

When I start my system, an alert from Backdoor.Hynet appears on the screen which says that my system is infected. Several times, I have ran full scanning in the PC but my anti-virus program doesn’t detects any threat. It is becoming extremely difficult for me to perform any task on the system. There are many unknown icons and files at desktop which comes back even after deletion. I am feeling helpless. Can you please help me to get rid of Backdoor.Hynet completely? Thanks a lot in advance.


Backdoor.Hynet is identified as backdoor Trojan which has recently created havoc amongst the users of Windows based PC. It will exploit the system vulnerabilities and carries ability to hide its presence internally. Once Backdoor.Hynet gets installed, you will detect strange activities in the system and it will not respond properly to your instructions. Initially, this threat can alter the system settings, DNS configurations, Host files etc. It is well known for opening a backdoor in the system. It tries to help its creators in accessing your personal data, email Ids, webcam secretly. Even more, it is designed in such a way which can keep its eyes on your online habits and when you will type any sensitive information then it can record them secretly. Whats worse, it can send all the collected data to the remote location servers with illegal aim. Thus, you should not allow Backdoor.Hynet to stay for long time in the PC.

Apart from harming your personal identity, Backdoor.Hynet can make your system completely useless. This threat comes with suspicious payloads to alter the registry keys. It helps the threat to execute automatically after the booting process of the system. It will also corrupt your stored files and makes them completely inaccessible. It will become difficult for the users to conduct any work on time due to weird behavior of the system. This threat can also disable Windows Firewall alert secretly in order to bring more malignant threats in the PC. You will be completely fed up with regular crashing or freezing of the operating system and sometimes, it will reboot during your important works. It can also create unwanted files and shortcuts on the desktop. So, what are you thinking for, if you have detected any of the symptoms of Backdoor.Hynet then remove it without making any delay.

Effective Guidelines To Remove EasyWeatherAlert Toolbar

Are you thinking to install EasyWeatherAlert Toolbar in your browser? Does it claims to provide instant weather report? Does it claims to be compatible with all the web browsers? If yes then you should read given post below. It contains complete information about EasyWeatherAlert Toolbar and the reasons why you should not install it.


What is EasyWeatherAlert Toolbar?

EasyWeatherAlert Toolbar has been developed by Mindspark Interactive Network, Inc. It is promoted as an useful add-on for the Google Chrome users. It claims to improve your access to local and national weather forecast in the USA. EasyWeatherAlert Toolbar is available at Chrome Web Store. It also claims to be compatible with Internet Explorer or Mozilla Firefox. In the first look, it may seems to useful in reality, it is considered as Potentially Unwanted Program. You must be aware that if you will proceed to install the toolbar without reading the terms and services carefully then lots of low quality programs will also invade in your system. 

EasyWeatherAlert Toolbar is capable to mislead the online session of the users to unknown pages and generate floods of bogus alerts. However, these advertisements and pop ups looks so attractive but clicking on the links will download potential stuffs in the PC. In fact, this add-on will secretly gather your cookies, browsing history, extensions, downloads and transfers them to the remote servers. Sometimes, it may stop you from accessing your favorite pages by showing annoying alerts.

Presence of EasyWeatherAlert Toolbar can also results to slow down in the running speed of the system functions in which you will also difficulty in opening a file on time. Even worse, it is responsible for performing changes in the default settings of the system without the users knowledge. Disable of installed programs is also possible and it may interrupt when you will attempt to install new softwares. Thus, it is essential for the users to uninstall EasyWeatherAlert Toolbar immediately after detection.


Tuesday, 27 September 2016

Delete Trojan.Redir: How To Eliminate Trojan.Redir Permanently

If your system has been infected with Trojan.Redir and you are having difficulty in removing it permanently then your search is over. This page contains the necessary information which will help you to remove Trojan.Redircompletely. You just need to follow the removal instructions in step-by-step manner.

Trojan.Redir: An Overview

Trojan.Redir is deemed as Trojan infection which is known for performing hazardous activities in the Windows PC. Once gets sneaked, it will start its malicious activities by changing the system settings. However, Trojan.Redir does not replicate itself in the PC but carries ability to leads it to destructive situations. Initially, it will take the system controls by changing the default settings and PC configurations. It can also disable the working of installed anti-virus programs to hide its presence for long time. In its presence, users may detect lots of unknown files, folders, shortcuts and icons at different location of the system. You will also notice that the running speed of the system functions such as start up, shut down, opening files, playing games, installing applications as well as Internet connection will start to degrade gradually. So, you should not allow Trojan.Redir to stay for long time in the PC.

More harms associated with Trojan.Redir:-
  • Monitors the online session of the users secretly.
  • Collects the senstive information and bypass them to the remote servers.
  • Changes desktop background, system setting s  and PC configurations.
  • Drops harmful codes in the Windows Registry Editor.
  • Shows low disk space when you will try to install new applications.
  • Disables Windows Firewall alert.
Hence, if you don’t want to face such troubles with your PC then take immediate action in the permanent removal of Trojan.Redir completely from the system.


Uninstall Super System Optimizer virus Immediately From PC

I want to know about Super System Optimizer virus. I have detected its presence in my PC but having troubles in removing it. In fact, I have deleted fake entries from registry editor but it creates again and again. It is becoming difficult for me to perform any task on the system. If you have any idea about the removal process of Super System Optimizer virus then please help me. All the suggestions will be highly appreciated.

What is Super System Optimizer virus?

Super System Optimizer virus has been created by Super System Utilities Inc. According to its official page, it is mostly advertised as the alternative of comic book character “Superman”. It pretends to be useful and claims to optimize the system performance, clearn the infected fils, work best foor the PC configurations and many more. An alert will ask you to buy the premium version by paying $40. At the first glance, it may seems like useful but wait. You need to know that it is a potentially unwanted program which can lure in the PC attached with the free softwares, spam emails, pen drives etc. Instead of providing protection to the system, it may introduce more nalignant threats which is not safe. Thus, we strongly advise our users to remove Super System Optimizer virus permanently if it is available in the system.

You need to reconsider before spending money on Super System Optimizer. It is capable to bring more malignant threats in the system which can affect its working performance and efficiency. Its presence can also damage the installed programs or softwaresby making them useless. You will detect unwanted modifications in the default settings of the system including DNS configurations, file system, privacy settings and many more. Additionally, it also targets the financial details of the users and carries ability to bypass them to the remote location servers. Thus, if you want to prevent your system from further hazards then remove Super System Optimizer virus as early as possible.


Monday, 26 September 2016

Remove Macissue.xyz: How To Delete Macissue.xyz Easily

Macissue.xyz is a browser hijacker which have capability to hijack different versions of Windows based PC. While surfing on the web, it will automatically appear on your screen and generates different types of pop ups, advertisements, banner ads, in-text links, contextual links etc. Macissue.xyz displays that your PC has been associated with errors and you need to resolve it immediately. On the screen, you will find a toll free number i.e. 1-844-507-3542. It will claim to provide immediate help from the technical experts.


Users must know that Macissue.xyz is completely an unsafe domain. The main goal of the hackers is to increase the network traffic of their sites. It may tactics on the users to pay for fake products and in the meanwhile, it can record your credential informations. It have capability to bypass your data, cookies or surfing history to the remote location servers. This hijacker can result extremely dangerous for the personal identity of the users. Thus, you should not allow Macissue.xyz to stay for long time in the system.

Besides this, Macissue.xyz will install fake extensions in your web browsers and alters the default settings. Normal working for the users will become extremely difficult and the running speed of all the functions will become difficult. Automatic changes in the default settings or PC configurations is also possible. It also comes with fake entries or malicious codes to modify the registry editor. This change help the threat to execute automatically in the PC. Whats worse, updated anti-virus programs or PC security tools will also fail to remove its existence. But it is essential for the users to remove Macissue.xyz in the early phase after detection.


Eliminate Discoveranswer.com easily in effective way


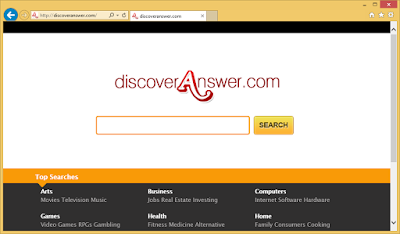
Discoveranswer.com is identified as questionable domain which pretends to be a legitimate site. It falls under the category of browser hijacker which is used by the hackers for advertising purpose. This page allows the users to download free software, games, movies etc which are available on the Internet. Discoveranswer.com carries ability to install itself in all the web browsers such as Mozilla Firefox, Google Chrome, Internet Explorer, Opera, Safari etc. This hijacker comes with harmful programs which can result dangerous for the system performance. Computer users must know that Discoveranswer.com has been created by the cyber crooks which carries ability to gain the system controls. It is capable to perform unwanted changes in the default settings of the system, browser, homepage, search engine etc. Misleading of the search results will become a common issue in its presence in which normal working is extremely difficult. Your screen will be filled with lots of advertisements, pop ups, warning messages, promotional alerts etc. Its long time presence can cause permanent freezing of the operating system. So, if you want to protect your system from being useless then you need to remove Discoveranswer.com without making any delay.

Block 1-888-750-9959 pop-up Instantly In Simple Method

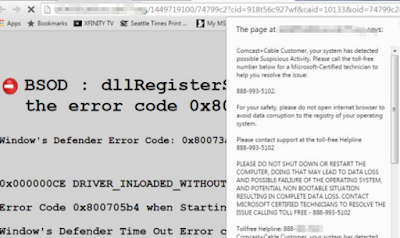
Imagine, you are working on your PC and suddenly a BSOD error like 1-888-750-9959 pop-up appears on your screen and your all task gets stopped. In such a case, many of the users tries to reboot the system but still detects such alerts. Usually, 1-888-750-9959 pop-up frightens the users by saying that your PC and personal information is not safe. It also asks the users to contact technical experts by calling on its toll free number. Nobody wants to face such troubles but these days, many of the Windows based PC users are experiencing this alert.


You should know that 1-888-750-9959 pop-up is just a scam of the third party hackers. You will get such warnings when your system will be infected with potentially unwanted programs. When you will call on these numbers then they will pretend to help you. They will use technology terms to confuse the users and convince them to buy their softwares. They claims to protect the system from all types of troubles. In order to get back their PC in normal mode, many users pay for the softwares. You will be shocked to know that they are capable to record your financial details when you will proceed to make payment. It can make you suffer from identity theft situations. Hence, try to avoid calling on 1-888-750-9959 anymore.

Whats more, clicking on 1-888-750-9959 pop-up will download more hazardous threats in the system which can create more troubles for your system. You will experience abnormal behavior in which working is quite difficult. Even, most of the installed softwares including security tools will stop responding. You will not be able to visit your favorite sites and crashing of the operating system will become a regular issue. Therefore, it is highly recommended to the users to remove the adware or unwanted programs immediately if you want to get rid of 1-888-750-9959 pop-up permanently.


Remove xml.olmeramarketing.com: Get Rid of xml.olmeramarketing.com

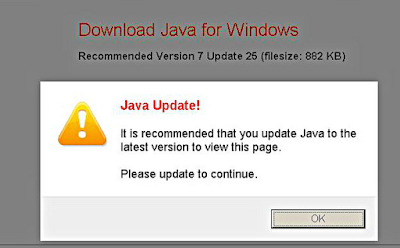
xml.olmeramarketing.com is deemed as unreliable domain which is basically used by the third parties. It comes under the category of browser hijacker which usually attacks different versions of Windows based PC. Once xml.olmeramarketing.com gets installed in the system, it will try to alter the homepage settings as well as search engines. It might be possible that your browser will be automatically redirected to its page. It displays a warning that “It is recommended that you update Java to the latest version to view this page”. Once you will click on OK button, it will display the free download link.


Be careful because xml.olmeramarketing.com is not a trustworthy domain. If you will proceed to install the software wiithout checking the EULA then additional low quality programs will also invade in the system. It is always mentioned in their privacy policy that by proceeding, you are allowing to install additional programs. It is also possible that it will record your cookies and display various types of unwanted advertisements. The only aim of the third party hackers is to drive more traffic on their page through illicit ways. So, we suggest our users to remove xml.olmeramarketing.com instantly after detection.

You will also detect fake extensions or add-ons in your browswe which will mislead your surfing to xml.olmeramarketing.com. It will become difficult for the users to visit any of their favorite or genuine sites. You will notice that the running speed of the system functions will start to degrade gradually in which you will not be able to open a single file on  time. Even, the installed anti-virus program will stop responding. This hijacker will hijack the system and also drops suspicious codes in the Windows Registry editor. Thus, what are you waiting for, if you have detected the presence of xml.olmeramarketing.com in your system then try to remove it immediately.


Saturday, 24 September 2016

Remove Indicator.dl-software.xyz Completely In Easiest Way

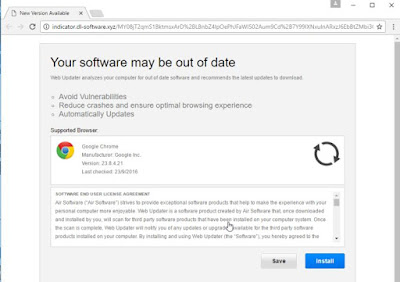
From last couple of days, I am detecting Indicator.dl-software.xyz during my online session. Whenever I try to open any other site, my browser gets diverted to its links. It displays warnings that my software is out of date and I need to install the updated version. Can you please provide information about Indicator.dl-software.xyz? Is it a legitimate site? Is it safe to download software from its links? Please help me.


Indicator.dl-software.xyz is a suspicious domain which has been created by the remote hackers. They use it for making promotion of their affiliate programs and tactics on the users to download the free versions. At the first glance, Indicator.dl-software.xyz will look like legitimate but do not trust it. In reality, it is considered as browser hijacker which is capable to hijack different versions of Windows PC. This page will generate alert i.e. “Your software may be out of date”. It convince the users to download the latest version to avoid vulnerabilities. Users must be aware that when you will click on Install button without reading its EULA (End Users Licensed Agreements) then lots of harmful stuffs will infiltrate in your PC. Therefore, do not visit Indicator.dl-software.xyz and if it is available in your PC then remove it quickly.

You may also find unreliable plug-ins, add-ons or extensions in your web browsers such as Mozilla Firefox, Google Chrome, Internet Explorer etc. It can also perform unwanted changes in the homepage settings and blocks the IP address. Besides this, it is capable to collect the cookies or browsing history of the compromised PC. It aims to gather the credential details of the users and sends them to the remote servers. You will also find extremely sluggish speed of various functions of the system in which opening a file is also difficult. It also comes with bogus codes and drops them in the registry edtor which helps it to execute automatically in th e system. Hence, do not ignore Indicator.dl-software.xyz for long time in your PC otherwise you have to pay heavy penalty in future.