Pages

Saturday, 24 September 2016

Remove Indicator.dl-software.xyz Completely In Easiest Way

From last couple of days, I am detecting Indicator.dl-software.xyz during my online session. Whenever I try to open any other site, my browser gets diverted to its links. It displays warnings that my software is out of date and I need to install the updated version. Can you please provide information about Indicator.dl-software.xyz? Is it a legitimate site? Is it safe to download software from its links? Please help me.
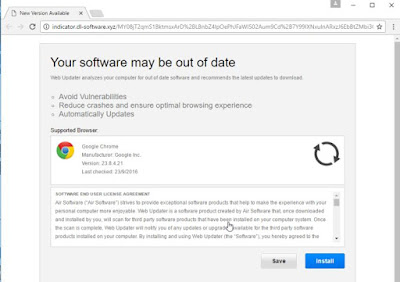


Indicator.dl-software.xyz is a suspicious domain which has been created by the remote hackers. They use it for making promotion of their affiliate programs and tactics on the users to download the free versions. At the first glance, Indicator.dl-software.xyz will look like legitimate but do not trust it. In reality, it is considered as browser hijacker which is capable to hijack different versions of Windows PC. This page will generate alert i.e. “Your software may be out of date”. It convince the users to download the latest version to avoid vulnerabilities. Users must be aware that when you will click on Install button without reading its EULA (End Users Licensed Agreements) then lots of harmful stuffs will infiltrate in your PC. Therefore, do not visit Indicator.dl-software.xyz and if it is available in your PC then remove it quickly.

You may also find unreliable plug-ins, add-ons or extensions in your web browsers such as Mozilla Firefox, Google Chrome, Internet Explorer etc. It can also perform unwanted changes in the homepage settings and blocks the IP address. Besides this, it is capable to collect the cookies or browsing history of the compromised PC. It aims to gather the credential details of the users and sends them to the remote servers. You will also find extremely sluggish speed of various functions of the system in which opening a file is also difficult. It also comes with bogus codes and drops them in the registry edtor which helps it to execute automatically in th e system. Hence, do not ignore Indicator.dl-software.xyz for long time in your PC otherwise you have to pay heavy penalty in future.


Get rid of +1 (877) 764-9824 pop-up Instantly

Many users  are annoyed with +1 (877) 764-9824 pop-up which displays warning alerts and claims to provide technical support. If you are one of them who is completely annoyed with bogus alerts then you have landed on perfect location. Go through the post below to learn the effective steps to block +1 (877) 764-9824 pop-up permanently.

+1 (877) 764-9824 pop-up is deemed as fake alert which is recently in news. It automatically appears on the screen during the surfing session of the users. It will say that your system is unsafe and your personal identity is at high security risk. +1 (877) 764-9824 pop-up claims to help the users by providing immediate support and convince them to call on its toll free number. However, this number may look like legitimate in the first look but it is not trustworthy. You need to be aware that it is a trick of the cyber crooks to promote their affiliate softwares. They will suggest you to buy malicious softwares and in the meantime, they can record your personal or financial details secretly. Hence, you should try to get rid of +1 (877) 764-9824 pop-up in the early phase after detection.
  • You will not be able to visit any legitimate sites.
  • Automatic redirection is possible.
  • Screen will be filled with unwanted pop ups and advertisements.
  • PC performance will become extremely sluggish.
  • Performs changes in the default settings of the system.
  • Downloads bundles of malicious threats or spywares.

+1 (877) 764-9824 pop-up is only caused by adware or potentially unwanted programs which can invade in the system without any prior notifications. It have capability to change the system settings and tries to gain the PC controls. Hence, if you are detecting +1 (877) 764-9824 pop-up regularly then try to remove the presence of unwanted programs immediately before it harms your PC severely.

Remove BEst DEealls 4 youuu Quickly In Simple Clicks

Are you detecting BEst DEealls 4 youuu during your shopping session? Does it claims to save your money? Does it displays attractive offers and discount coupons on the screen? Do not trust all these alerts because it is displayed by adware programs. This alerts only means that your system is infected. We aims to help the users to protect their system. In this guide, you will learn the simplest method to block BEst DEealls 4 youuu alerts permanently. So, try to follow the guidelines carefully.


BEst DEealls 4 youuu is recognized as adware program which can penetrate in the system bundled with the free programs, spam emails, infected pen drives etc. Once sneaks in the PC, it will install its own extension in Google Chrome, add-ons in Mozilla Firefox or Internet explorer. BEst DEealls 4 youuu also tries to perform changes in the default settings even without the users consent. When you will start surfing the web, it will appear on the screen with variety of attractive deals, offers, discount coupons etc. It claims to help the users in the shopping session in order to save their money. However, these alerts seems attractive and useful but reality is completely different. You will be shocked to know that it is just a trick of the hackers to earn illegal profits. When you will click on its links and proceed for making payment then hackers will secretly record your financial details. BEst DEealls 4 youuu can result extremely dangerous for your personal identity. So, try to remove it as early as possible.

Whats more, BEst DEealls 4 youuu also allows the users download some freewares which contains infectious stuffs. It carries ability to block your IP address and doesn’t allow the users to access their favorite sites. The running speed of the PC will become extremely sluggish in which opening a file is also a difficult task. Additionally, you will detect unwanted changes in the default settings of the system and it will behave strangely to your instructions. Thus, if you don’t want to pay heavy penalty in future then remove BEst DEealls 4 youuu completely without wasting a single moment.

Uninstall www.stamplive.com Permanently In Few Minutes

If your surfing session automatically gets diverted to www.stamplive.com then definitely your system has been hijacked. No need to panic, we are here to guide you. In this post, we are providing complete and detailed information about www.stamplive.com. You will also learn the simplest method to get rid of it permanently. Thus, read the given post carefully.


Complete Analysis About www.stamplive.com:-

www.stamplive.com is a redirect virus which always misleads the users to suspicious pages of the third parties. It does not require any permission to invade in the targeted system and carries ability to perform changes in the homepage settings. You may detect some unknown extensions in your web browsers such as Google Chrome, Mozilla Firefox, Internet Explorer etc. Clicking on such extensions will redirect you to www.stamplive.com automatically. You will find different types of alerts on the screen which may ask you to download free software, movies, videos, music etc. Beware because clicking on these links will allow harmful threats to invade in your system. When you will proceed to install free software without reading their privacy policy then several low quality programs will also sneak secretly. Thus, it is essential for the users to remove www.stamplive.com instantly after detection.

Due to the presence of www.stamplive.com in the system, you will notice slow down of all the basic functions such as start up, turn off, playing games,, installing applications, Internet connection etc. It also brings suspicious codes to change the registry entries of the system. Whats more, it have capability to keep its eyes on the online activities of the users in order to gather their sensitive details. Even worse, it is capable to bypass your financial or personal details to the remote location servers. Long time presence of www.stamplive.com can leads your PC to destructive situations and harms your personal identity. So, don’t make any delay in removing www.stamplive.com completely from the infected PC.


Remove Searchvvay.com: Tips to delete Searchvvay.com

Today I was surprised to see Searchvvay.com as my search engine. I tried to open Google but again my browser got redirected to its homepage. I was strange for me so I rebooted my PC but still faced the same issue. Why I am unable to open any other site? What is the reason behind such unwanted changes in the system settings? Could you please provide complete details about Searchvvay.com? Thank you so much in advance.


What is Searchvvay.com?

Searchvvay.com is identified as low quality search engine which looks exactly like a genuine domain. On its homepage, you will find a search bar which claims to help you in searching anything on the web. If you have detected Searchvvay.com in your browser then you need to know that your browser has been hijacked. It is a browser hijacker which can secretly invade in the system when user visits any suspicious sites or downloads free software without checking its EULA. Initially, it will perform changes in your browser settings and appears as default homepage. It can also stop the users from visiting their favorite or any legitimate sites. Using its search bar will mislead you to malignant pages where unstoppable pop ups or advertisements will appear on the screen. Thus, experts advised the users to remove Searchvvay.com in the early phase after detection.

More hazards associated with Searchvvay.com:-
  • Disables Windows Firewall and other PC securities.
  • Shows various types of annoying ads, pop ups, warning messages etc.
  • Downloads bundles of potential stuffs to harm the system.
  • Modifies the default settings of the PC.
  • Degrades the running performance of various functions.
  • Monitors the users activities with illegal aim.
Searchvvay.com is also responsible for modification in the registry entries. In its presence, you will notice that updated security programs will become inaccessible. Moreover, it is capable to keep its eyes on your online session and steals all the sensitive information including banking details, passwords, credit card information and many more. Therefore, don’t waste a single moment in removing Searchvvay.com completely from the infected system.

Get Rid of Critical System Failure popups Immediately

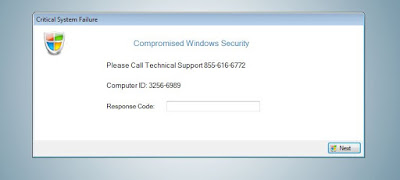
Yesterday I was surfing the web then suddenly Critical System Failure popups appeared on the screen. It displayed that my Windows is compromised and I need to enter the response code. I found a toll free number in the pop up. Due to Critical System Failure popups, now I am unable to perform any activity on the system. Can you help me to get rid of Critical System Failure popups permanently? Lots of thanks in advance.


Know About Critical System Failure popups:-

Critical System Failure popups are fake alert which is not real. These alerts are usually displayed by the adware programs which may sneak in the system without the users consent. These alerts will appear on your screen and tries to frighten the innocent users. It is also possible that Critical System Failure popups displays a toll free number i.e. 855-616-6772 and claims to provide instant technical support. Users needs to know that it is a bogus alert so try to avoid calling on its number. Instead of providing support to the users, it will bring more damage. You  will be fed with floods of warning alerts and error messages on the screen. Thus, if you are detecting Critical System Failure popups then try  to remove the adware programs completely from the PC.

Harmful Consequences of Critical System Failure popups:-
  • Misleads the users to unreliable pages.
  • Installs lots of malignant stuffs in the system.
  • Degrades the running speed of the compromised PC.
  • Monitors the users activities and send their sensitive data to the third party hackers.
  • Disables the security programs of the system.

Thursday, 22 September 2016

Complete Guide To Remove Trojan.Desurou

If you are unable to remove Trojan.Desurou completely from your PC and looking for the easiest removal guidelines thenn your search is over. This post is ready to help you. Follow the simple steps which are given below. 

 Know Details About Trojan.Desurou 

Trojan.Desurou is identified as malicious Trojan which is capable to exploit the vulnerabilities of the PC. It doesn’t matter that you have installed updated anti-virus program, it will enter in the system by breaking the securities. Recently, the presence of Trojan.Desurou has been detected by millions of the system across the world. Once sneaks in the system, it willl degrades the running performance of all the basic functions including Internet connection. This threat will also add malicious codes in the registry editor of the compromosed PC which helps it to execute automatically. 

Additionally, Trojan.Desurou is also known for corrupting the stored files or documents of the users. You may detect lots of unknown icons, folders, shortcuts on the desktop which will be difficult to remove manually. The file size of the threat varies in different PC but it uses huge space in the memory. When the users attempts to install new application, it will generate the message of insufficient space. 

Besides this, Trojan.Desurou also helps its creators to earn illegal profits. Without your consent, it will try to gain your sensitive informations such as bank account number, password, login details, credit card details etc. Whats more, it is capable to bypass your information to the third party servers which is completely unsafe for the personal identity of the users. So, what are you waiting for, take quuick actions in the removal of Trojan.Desurou permanently from the PC.

Usr0@riseup.net Removal Guidelines From Infected PC

Usr0@riseup.net is a nasty ransomware which is recently in news for performing malicious activities in the system. It can lurk without the users approval via malicious downloads, spam emails, clicking on suspicious links etc. As soon as Usr0@riseup.net got installed in the system, it will drop malicious codes to encrypt all your media files which includes photos, videos, documents, files, texts etc. This threat can stop all the program execution of the PC by locking various installed programs. After encrypting the encryption process, it will create a TXT file on the desktop. This file will contain some instructions and it will ask you to buy a decryption key. 

Usr0@riseup.net shows various types of warning messages that if you will try to use any other method to decrypt the files then it can create troubles for you. It forces the users to send 1.24 BTC (About 50500 RU) to get the decryption key. You may also find alert which will say that if you will not pay the fine within the given period then you will loose all the chances to restore your data. 

Users needs to know that it is just a trick used by the third party hackers to gain illegal profits. The worst part is that they can collect your credential details and use them for cyber crime activities. Paying the amount is neither safe nor helpful because it will never help you to decrypt the files. You need to remove Usr0@riseup.net immediately from the PC after detection. Here we are providing the removal steps which you can follow to protect your system.

Saturday, 17 September 2016

Learn Simple Tips To Remove CryLocker Ransomware


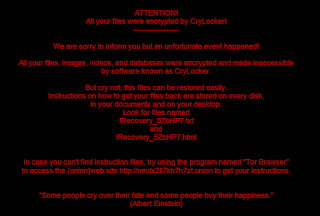
CryLocker Ransomware is referred as harmful ransomware which is also known as CSTO (Central Security Treatment Organization). It is another file encryption ransomware which carries ability to encrypts the files the infected PC. This means that it will lock your PC files and demands ransom amount to decrypt them. CryLocker Ransomware When the users attempts to open their files, it generate alerts that you need to pay the ransom amount of 1.1. bit-coins (Approx 625 USD). It is also possible that it may divert you to suspicious sites and tactics on the users to proceed for the payment. Don’t get trapped in the scam of the hackers by trusting the alerts displayed by CryLocker Ransomware. 

CryLocker Ransomware can find its own method to infiltrate in the system by executing malignant codes or comes attached with spam emails. This ransomware can easily take the system controls and doesn’t allow the users to perform any task on time. It can also create ransom note on the desktop and asks the users to follow its instructions. Beware with such alerts because it can result dangerous for your PC. In reality, its only objective is to earn profits through illegal ways. Thus, if you have detected CryLocker Ransomware in your system then try to remove it permanently without wasting a single moment.

Remove SONAR.SuspBeh!gen57: Protect Your PC From SONAR.SuspBeh!gen57

Brief Details About SONAR.SuspBeh!gen57: 

SONAR.SuspBeh!gen57 is a detection in Trojan category. According to the experts, it can infect different version of Windows based PC such as Windows XP, Vista, 7, 8, 10 etc. This threat will secretly attack your PC and tries to exploit its vulnerabilities. It is known for modifying the system settings and monitors the behavior secretly. SONAR.SuspBeh!gen57 is capable to modify the registry entries, so victims notice changed behavior of the PC. In fact, you will have troubles in opening the program files as it can corrupt the data. This threat can also create several infected folders and icons at different destinations of the system. 


Once SONAR.SuspBeh!gen57 invades in the system, you will experience slow down in the speed of the system performance. Its presence will also cause automatic shut down of the infected system which is quite annoying. This program takes huge amount of space in the system memory. It also stops the users from installing new application software. Whats worse, your installed anti-virus program will stop responding and generate floods of warning messages or error alerts on the screen. 

Users needs to know that SONAR.SuspBeh!gen57 has been created by the cyber hackers. It aims to gather the personal and financial details of the users. Even more, this threat can bypass your data to the remote location servers and allows the third parties to use them for illegal purpose. Do not ignore it for long time otherwise it will make your PC almost useless. Therefore, users are suggested to perform full scanning in the system and remove SONAR.SuspBeh!gen57 ASAP.